
Anthropic said Claude Mythos would remain restricted. The company was clear about it: stronger safeguards were needed before any general release, and for now the model would stay limited to roughly 40 selected organizations through Project Glasswing.
The next day, users started seeing “Mythos 1” inside Claude Code.
The model appeared in the UI briefly, with a preview label reading “claude-mythos-1-preview,” then disappeared again. TestingCatalog found new strings in the source code: “Access to the Claude Mythos model in Claude Code and Claude Security.” Screenshots circulated on X. Then the traces were gone.
This would be easy to dismiss as an internal testing slip if it hadn’t happened before. It has happened before. Multiple times.
Table of Contents
What actually appeared
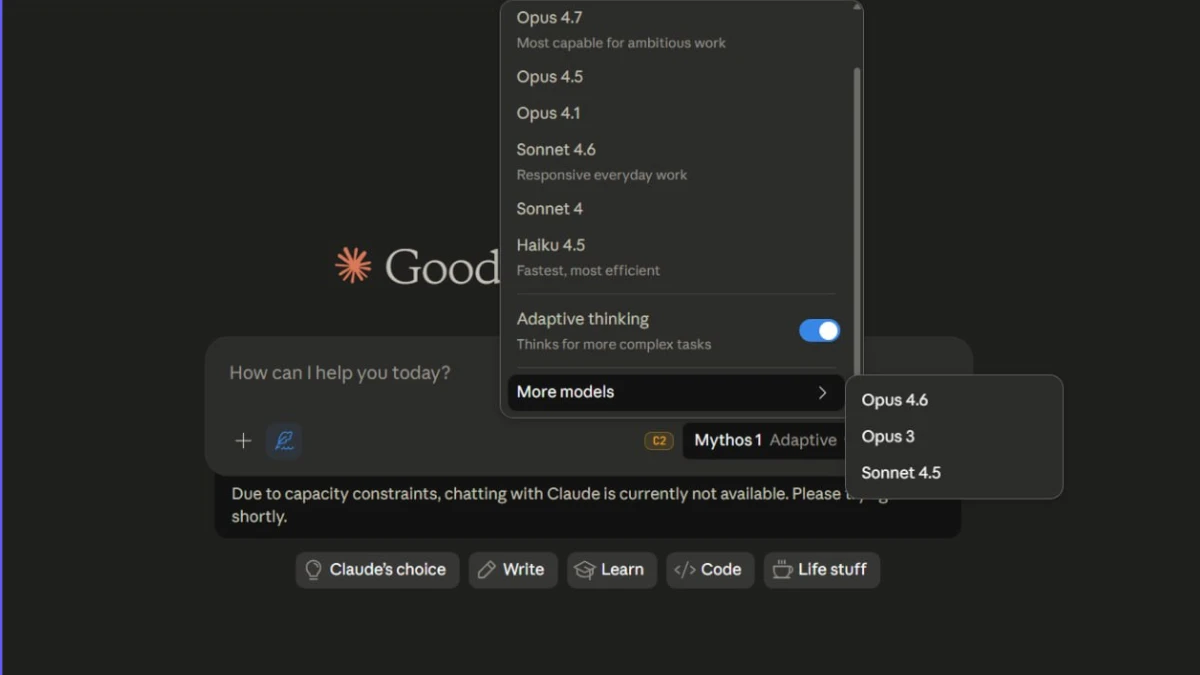
The sighting wasn’t a rumor. Users briefly saw the Mythos 1 model listed directly in the Claude Code interface, the same tool developers use daily for coding workflows. The label “claude-mythos-1-preview” is specific enough to suggest an actual product build.
The source code strings found alongside it are equally specific. “Access to the Claude Mythos model in Claude Code and Claude Security” reads like integration copy, the kind of text that gets written when a feature is being prepared for users.
Claude Security’s side of this is also getting structural work done quietly. A new dashboard is being built that surfaces discovered vulnerabilities, with seven and thirty day historical charts and deeper triage results. That’s not the work you do for a product that isn’t moving toward broader availability. That’s the work you do when you’re getting something ready.
This isn’t the first time
The Claude Code appearance is the most visible sighting but it’s the third time Mythos traces have surfaced somewhere they weren’t supposed to be.
Before this, references appeared through AWS and Google Cloud vulnerability discovery systems. Before that, reports emerged of unauthorized users briefly accessing parts of the model. Each time, Anthropic removed the traces. Each time, the company’s public position remained that Mythos was restricted and would stay that way until safeguards were stronger.
Three separate appearances across different platforms over a short period stops looking like accidents. It starts looking like a staged rollout that hasn’t been announced yet, or a model that’s being quietly tested in production environments while the public messaging stays cautious. Neither reading makes Anthropic look careless. Both suggest the difference between what the company says publicly and what it’s actually preparing.
Related: Anthropic’s Mythos Just Helped Find macOS vulnerability That Could Break Apple’s Security Protections
Why Anthropic is being too careful
What Mythos actually did under Project Glasswing is the reason.
In under a month, working with more than 50 major developers and infrastructure partners, the model identified over 10,000 high-severity or critical software vulnerabilities. The systems involved included Cloudflare, Firefox, and OpenBSD. One finding was a bug in OpenBSD that had gone undetected for 27 years. The model also reportedly helped a partner bank block a $1.5 million cryptocurrency fraud attempt by flagging suspicious behavior before funds moved.
Those are defensive wins. The same capability that finds a 27-year-old bug in a security library can also be pointed at systems without permission. A model this capable at finding vulnerabilities is genuinely dual-use in a way that most AI safety discussions treat as hypothetical. For Mythos it’s just a description of what the model does.
The open source community’s reported reaction to the volume of findings, “please stop finding vulnerabilities, we can’t keep up,” points at a different problem. Speed of discovery has outpaced speed of remediation. Anthropic is now reportedly building patch generation tools alongside the vulnerability scanner, which suggests they understand that finding 10,000 bugs is only useful if someone can fix them.
What the pattern actually means
Anthropic’s public position and the product signals are pointing in different directions.
The official line is that Mythos remains restricted, safeguards are still being developed, and general release is a future event with no firm date. That’s been consistent. What’s also been consistent is Mythos showing up in places it wasn’t announced, across three different platforms, each time briefly and each time removed.
The most straightforward reading is a staged rollout that hasn’t been formally announced. Claude Code and Claude Security are controlled environments with existing enterprise user bases. Testing Mythos there before a broader release is exactly what a cautious rollout looks like. The new Claude Security dashboard, the source code strings, the preview label on Mythos 1, none of that is accidental infrastructure.
What we don’t know is the timeline. Anthropic hasn’t said when safeguards will be strong enough, what those safeguards actually are, or what a general release would look like in practice. Claude Opus 4.8 is also reportedly in internal evaluation with select partners, which would fit a broader product cadence if it lands alongside a Mythos expansion.
For now the clearest thing that can be said is a model Anthropic describes as not ready for the public keeps appearing in public-facing products.